Build Secure APIs in Minutes
Everything you need to ship production APIs
From authentication to documentation, we handle the infrastructure so you can focus on building features.
- 1
Authentication Built In
API keys, OAuth 2.0, and JWT tokens work out of the box. Secure endpoints with a single line of configuration—no auth boilerplate to maintain.
- 2
Smart Rate Limiting
Protect your infrastructure with flexible rate limits per endpoint, user, or API key. Set quotas in the dashboard and enforce them globally across all regions.
- 3
Beautiful OpenAPI Docs
Interactive documentation generated automatically from your code. Clients can test endpoints, see examples, and download SDKs—all from one beautiful interface.
- 4
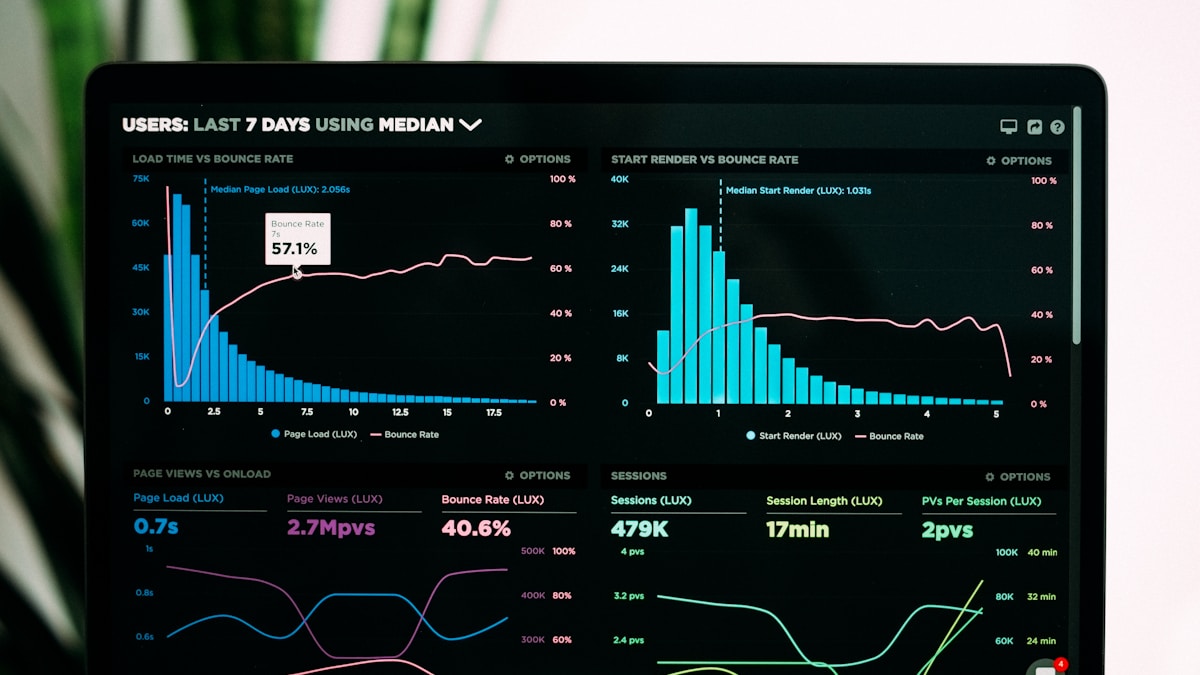
Real-Time Analytics
Monitor every request with detailed logs, latency histograms, and error tracking. Identify bottlenecks and optimize performance with actionable insights.
Weekly active teams
import { api } from '@apiplatform/core'; export const getUser = api.get('/users/:id', { auth: 'required', rateLimit: { requests: 100, window: '1m' }, handler: async (req) => { return db.users.findById(req.params.id); } });Under the hood
The architecture that scales from prototype to production
Edge authentication
API keys and tokens are validated at the edge in under 2ms. Invalid requests never touch your origin—saving bandwidth and compute while blocking attacks at the perimeter.
Distributed rate limiting
Rate limit state syncs across 200+ edge locations using CRDTs. Limits are enforced globally with single-digit millisecond accuracy, preventing quota abuse without a central bottleneck.
Zero-config observability
Every request is logged with full context—headers, timing, auth principal, and response codes. Query logs in real-time or export to your data warehouse for compliance audits.
Auto-generated OpenAPI specs
Type definitions in your code become interactive docs automatically. Schema validation runs on every request, catching malformed payloads before they reach your handlers.
Request path